Data Processing Agreement

This Data Processing Agreement (“DPA”) forms part of the Terms of Use (or other similarly titled written or electronic agreement addressing the same subject matter) (“Agreement”) between Customer (as defined in the Agreement) and “TLM Inside Sales Support Pvt.Ltd” under which the Processor provides the Controller with the software and services (the“Services”). The Controller and the Processor are individually referred to as a “Party” and collectively as the “Parties”.

The Parties seek to implement this DPA to comply with the requirements of EU & UK GDPR (defined hereunder) in relation to Processor’s processing of Personal Data (as defined under the EU & UK GDPR) as part of its obligations under the Agreement.

This DPA shall apply to Processor’s processing of Personal Data, provided by the Controller as part of Processor’s obligations under the Agreement.

Except as modified below, the terms of the Agreement shall remain in full force and effect.  

1.  Definitions

Terms not otherwise defined here in shall have the meaning given to them in the EU & UK GDPR or the Agreement. The following terms shall have the corresponding meanings assigned to them below:

2.  Purpose of this Agreement

This DPA sets out various obligations of the Processor in relation to the Processing of Personal Data and shall be limited to the Processor’s obligations under the Agreement. If there is a conflict between the provisions of the Agreement and this DPA, the provisions of this DPA shall prevail.

3.  Categories of Personal Data and Data Subjects

The Controller authorizes permission to the Processor to process the Personal Data to the extent of which is determined and regulated by the Controller. The current nature of the Personal Data is specified in Annex I to Schedule 1 to this DPA.

4.  Purpose of Processing

The objective of Processing of Personal Data by the Processor shall be limited to the Processor’s provision of the Services to the Controller and or its Client, pursuant to the Agreement.

5.  Duration of Processing

The Processor will Process Personal Data for the duration of the Agreement, unless otherwise agreed upon in writing by the Controller.

6.  Data Controller’s Obligations
7.   Data Processor’s Obligations
8.   Data Secrecy
9.    Audit Rights
10.   Mechanism of Data Transfers
11.   Sub-processors
12. Personal Data Breach Notification
13. Return and Deletion of Personal Data
14. Technical and Organizational Measures

CCPA” means the California Consumer Privacy Act of 2018, Cal. Civ. Code § 1798.100 et seq., as amended, including by the California Privacy Rights Act of 2020 (CPRA), which enhances consumer privacy rights and imposes obligations on businesses collecting personal information of California residents

15. CCPA / CPRA COMPLIANCE OBLIGATIONS
16. DATA SUBJECT RIGHTS AND ASSISTANCE
17. SUB-PROCESSORS
SCHEDULE 1
ANNEX I
A.LIST OF PARTIES
Data Exporter(s):

Name : Customers (As set forth in the relevant order form).

Address : As set forth in the relevant Order Form.

Contact person’s name, position, and contact details : As set forth in the relevant Order Form.

Activities relevant to the data transferred under these Clauses : Recipient of the Services provided by TLM Inside Sales Support Pvt.Ltd in accordance with the Agreement.

Signature and date : Signature and date are set out in the Agreement.

Role Controller/ Processor) : Controller

Data Importer(s):

Name : TLM Inside Sales Support Pvt.Ltd

Address : 102 Wing 5 Rajat Sankul Appt, Baidhyanath square Nagpur MH 440018

Contact person’s name : Pratik Shende

Position : CISO/DPO

Contact details : Pratik.shende@tlminsidesales.com

Activities relevant to the data transferred under these Clauses : Provision of the Services to the Customer in accordance with the Agreement.

Activities relevant to the data transferred under these Clauses : Provision of the Services to the Customer in accordance with the Agreement.

Role(controller/processor) : Processor.

B.DESCRIPTION OF TRANSFER

Categories of data subjects whose personal data is transferred : Customer’s authorized users of the Services.

Categories of personal data transferred : Name, Address, Date of Birth, Age, Education, Email, Gender, Image, Job, Language, Phone, Related person, Related URL, User ID, Username.

Sensitive data transferred (if applicable) and applied restrictions or safeguards that fully take into consideration the nature of the data and the risks involved, such as for instance strict purpose limitation, access restrictions (including
access only for staff having followed specialized training), keeping a record of access to the data, restrictions for onward transfers or additional security measures: No sensitive data collected.

The frequency of the transfer (e.g., whether the data is transferred on a one-offor continuous basis) : Continuous basis.

Nature of the processing : <ADD>

Purpose(s) of the data transfer and further processing : The purpose of the transfer is to facilitate the performance of the Services more fully described in the Agreement and accompanying order forms.

The period for which the personal data will be retained, or, if that is notpossible, the criteria used to determine that period : The period for which the Customer Personal Data will be retained is more fully described in the Agreement, Addendum, and accompanying order forms.

For transfers to (sub-) processors, also specify subject matter, nature, and duration of the processing : The subject matter, nature, and duration of the Processing more fully described in the Agreement, Addendum, and accompanying order forms.

C.COMPETENT SUPERVISORY AUTHORITY

Data exporter is established in an EEA & UK country. The competent supervisory authority is as determined by application of Clause 13 of the EU SCCs.

ANNEX II

TECHNICAL AND ORGANISATIONAL MEASURES INCLUDING TECHNICAL AND ORGANISATIONAL MEASURES TO ENSURE THE SECURITY OF THE DATA

Description of the  technical and organisational security measures implemented by TLM Inside Sales Support Pvt.Ltd as the data processor/data importer to ensure an appropriate level of security, taking into account the nature, scope, context, and purpose of the processing, and the risks for the rights and freedoms of natural persons.

Security
  • Security Management System.
    • Organization. TLM Inside Sales Support Pvt.Ltd designates qualified security personnel whose responsibilities include development, implementation, and ongoing maintenance of the Information Security Program.  
    • Policies. Management reviews and supports all security related policies to ensure the security, availability, integrity and confidentiality of Customer Personal Data. These policies are updated atleast once annually.
    • Assessments. TLM Inside Sales Support Pvt.Ltd engages a reputable independent third-party to perform risk assessments of all systems containing Customer Personal Data at least once annually.  
    • Risk Treatment. TLM Inside Sales Support Pvt.Ltd maintains a formal and effective risk treatment program that includes penetration testing, vulnerability management and patch management to identify and protect against potential threats to the security, integrity or confidentiality of Customer Personal Data.  
    • Vendor Management. TLM Inside Sales Support Pvt.Ltd maintains an effective vendor management program.  
    • Incident Management. TLM Inside Sales Support Pvt.Ltd reviews security incidents regularly, including effective determination of root cause and corrective action.  
    • Standards. TLM Inside Sales Support Pvt.Ltd operates an information security management system that complies with the requirements of ISO/IEC 27001:2022 standard.  
  • Personnel Security.
    • TLM Inside Sales Support Pvt.Ltd personnel are required to conduct themselves in a manner consistent with the company’s guidelines regarding confidentiality, business ethics, appropriate usage, and professional standards. TLM Inside Sales Support Pvt.Ltd conducts reasonably appropriate background checks on any employees who       will have access to client data under this Agreement, including in relation to employment history and criminal records, to the extent legally permissible and in accordance with applicable local labor law, customary practice and statutory regulations.  
    • Personnel are required to execute a confidentiality agreement in writing at the time of hire and to protect Customer Personal Data at all times. Personnel must acknowledge receipt of, and compliance with, TLM Inside Sales Support Pvt.Ltd’s confidentiality, privacy and security policies. Personnel are provided with privacy and security training on how to implement and comply with the Information Security Program. Personnel handling Customer Personal Data are required to complete additional requirements appropriate to their role (e.g., certifications). TLM Inside Sales Support Pvt.Ltd’s personnel will not process Customer Personal Data without authorization.  
  • Personnel Security.
    • Access Management. TLM  Inside Sales Support Pvt.Ltd maintains a formal access management process for the request, review, approval and provisioning of all personnel with access to Customer Personal Data to limit access to Customer Personal Data and systems storing, accessing or transmitting Customer Personal Data to properly authorized persons having a need for such access. Access reviews are conducted periodically to ensure that       only those personnel with access to Customer Personal Data still require it.  
    • Infrastructure Security Personnel. TLM Inside Sales Support Pvt.Ltd has, and maintains, a security policy for its personnel, and requires security training as part of the training package for its personnel. TLM Inside Sales Support Pvt.Ltd’s infrastructure security personnel are responsible for the ongoing monitoring of TLM Inside Sales Support Pvt.Ltd’s security infrastructure, the review of the Services, and for responding to security incidents.  
    • Access Control and Privilege Management. TLM Inside Sales Support Pvt.Ltd’s and Customer’s administrators and end users must authenticate themselves via a Multi-Factor authentication system or via a single sign on system in order to use the Services  
    • Internal Data Access Processes and Policies – Access Policy. TLM Inside Sales Support Pvt.Ltd’s internal data access processes and policies are designed to protect against unauthorized access, use, disclosure, alteration or destruction of Customer Personal Data. TLM Inside Sales Support Pvt.Ltd designs its systems to only allow authorized persons to access data they are authorized to access based on principles of “least privileged” and “need to know”, and to prevent others who should not have access from obtaining access. TLM Inside Sales Support Pvt.Ltd requires the use of unique user IDs, strong passwords, two factor authentication and carefully monitored access lists to minimize the potential for unauthorized account use. The granting or modification of access rights is based on: the authorized personnel’s job responsibilities; job duty requirements necessary to perform authorized tasks; a need to know basis; and must be in accordance with TLM Inside Sales Support Pvt.Ltd’s internal data access policies and training. Approvals are managed by workflow tools that maintain audit records of all changes. Access to systems is logged to create an audit trail for accountability. Where passwords are employed for authentication (e.g., login to workstations), password policies follow industry standard practices. These standards include password complexity, password expiry, password lockout, restrictions on password reuse and re-prompt for password after a period of inactivity.    
  • Data Center and Network Security
    • Data Centers.  
      • Infrastructure. TLM Inside Sales Support Pvt.Ltd has AWS as its data center.
      • Resiliency. Multi Availability Zones are enabled on AWS and TLM Inside Sales Support Pvt.Ltd conducts Backup Restoration Testing on regular basis to ensure resiliency.      
      • Server Operating Systems. TLM Inside Sales Support Pvt.Ltd’s servers are customized for the application environment and the servers have been hardened for the security of the Services. TLM Inside Sales Support Pvt.Ltd employs a code review process to increase the security of the code used to provide the Services and enhance the security products in production environments.        
      • Disaster Recovery.TLM Inside Sales Support Pvt.Ltd replicates data over multiple systems to help to protect against accidental destruction or loss. TLM Inside Sales Support Pvt.Ltd has designed and regularly plans and tests its disaster recovery programs.      
      • Security Logs. TLM Inside Sales Support Pvt.Ltd’s systems have logging enabled to their respective system log facility in order to support the security audits, and monitor and detect actual and attempted attacks on, or intrusions into, TLM Inside Sales Support Pvt.Ltd’s systems.
      • Vulnerability Management. TLM Inside Sales Support Pvt.Ltd performs regular vulnerability scans on all infrastructure components of its production and development environment. Vulnerabilities are     remediated on a risk basis, with Critical, High and Medium security patches for all components installed as soon as commercially possible.      
    • Networks and Transmission.
      • Data Transmission.Transmissions on production environment are transmitted via Internet standard protocols.  
      • External Attack Surface. AWS Security Group which is equivalent to virtual firewall is in place for Production environment on AWS.  
      • Incident Response. TLM Inside Sales Support Pvt.Ltd maintains incident management policies and       procedures, including detailed security incident escalation procedures. TLM Inside Sales Support Pvt.Ltd monitors a variety of communication channels for security incidents, and TLM Inside Sales Support Pvt.Ltd’s  security personnel will react promptly to suspected or known incidents, mitigate harmful effects of such security incidents, and document such  security incidents and their outcomes.  
      • Encryption Technologies. TLM Inside Sales Support Pvt.Ltd makes HTTPS encryption (also referred to as SSL or TLS) available for data in transit.  
    • Data Storage, Isolation, Authentication, and Destruction. TLM Inside Sales Support Pvt.Ltd stores data in a multi-tenant environment on AWS servers. Data, the Services database and file system architecture are replicated between multiple availability zones on AWS. TLM Inside Sales Support Pvt.Ltd logically isolates the data of different customers. A central authentication system is used across all Services to increase uniform security of data. TLM Inside Sales Support Pvt.Ltd ensures secure disposal of Client Data through the use of a series of data destruction processes.
ANNEX III

LIST OF SUB-PROCESSORS

The controller has authorized the use of the following sub-processors:
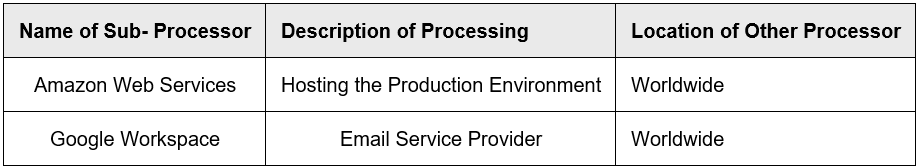
Table of TLM sub-processors: Amazon Web Services and Google Workspace